HSIA Gateway
Captive Portal.
Captive Portal, Voucher & Guest WiFi — Built for HSIA.
Built for staff villages, schools and hotels. Guest WiFi, vouchers, DHCP, DNS and firewall are integrated from the start. Add Zenarmor when you need advanced security.
EdgeCue EC-10000 — net in from above, every profile served through the portal.
HSIA Gateway, Built for Hospitality & High Density
Captive portal, voucher and Guest WiFi come first. DHCP, DNS and firewall are built in. If you need deeper application checks, you can add Zenarmor. Otherwise you keep things simple.
Voucher & Guest WiFi
Your own login page with your logo. Each voucher can limit speed, time and how many devices can connect, and you can check who is online.
DHCP & DNS Included
Give each VLAN its own DHCP range and fixed IPs where needed. The DNS runs on the same box, so you do not need extra servers.
Firewall at the Edge
NAT, country blocking and VLAN rules are built in. Most sites do not need a separate firewall.
Zenarmor (Optional)
Need to inspect apps or encrypted traffic? Add Zenarmor as a paid add-on and use it only where it helps.
Purpose-Built HSIA
with Captive Portal
EdgeCue is NETCUE's HSIA Gateway. It is a captive portal first box with the basics built in. We built it for staff villages, campuses and hotels, and we can adjust the ports, size and casing to fit your site. HSIA is the core, not an extra.
Whether it is a 5,000-bed village in Dubai, a university in Oman or a hotel in Abu Dhabi, you get your own branded Guest WiFi, voucher access, DHCP, DNS and firewall from one box. Add Zenarmor only if you need deeper filtering.
- No per-user licensing fees — flat appliance pricing
- Bug fixes and ongoing maintenance via NETCUE Care
- Firmware updates as a paid service under Enterprise Support
- UAE-based engineering support & on-site deployment
- Compatible with all ISPs across UAE & GCC
- Native integration with AccessCue RADIUS & NexusCue
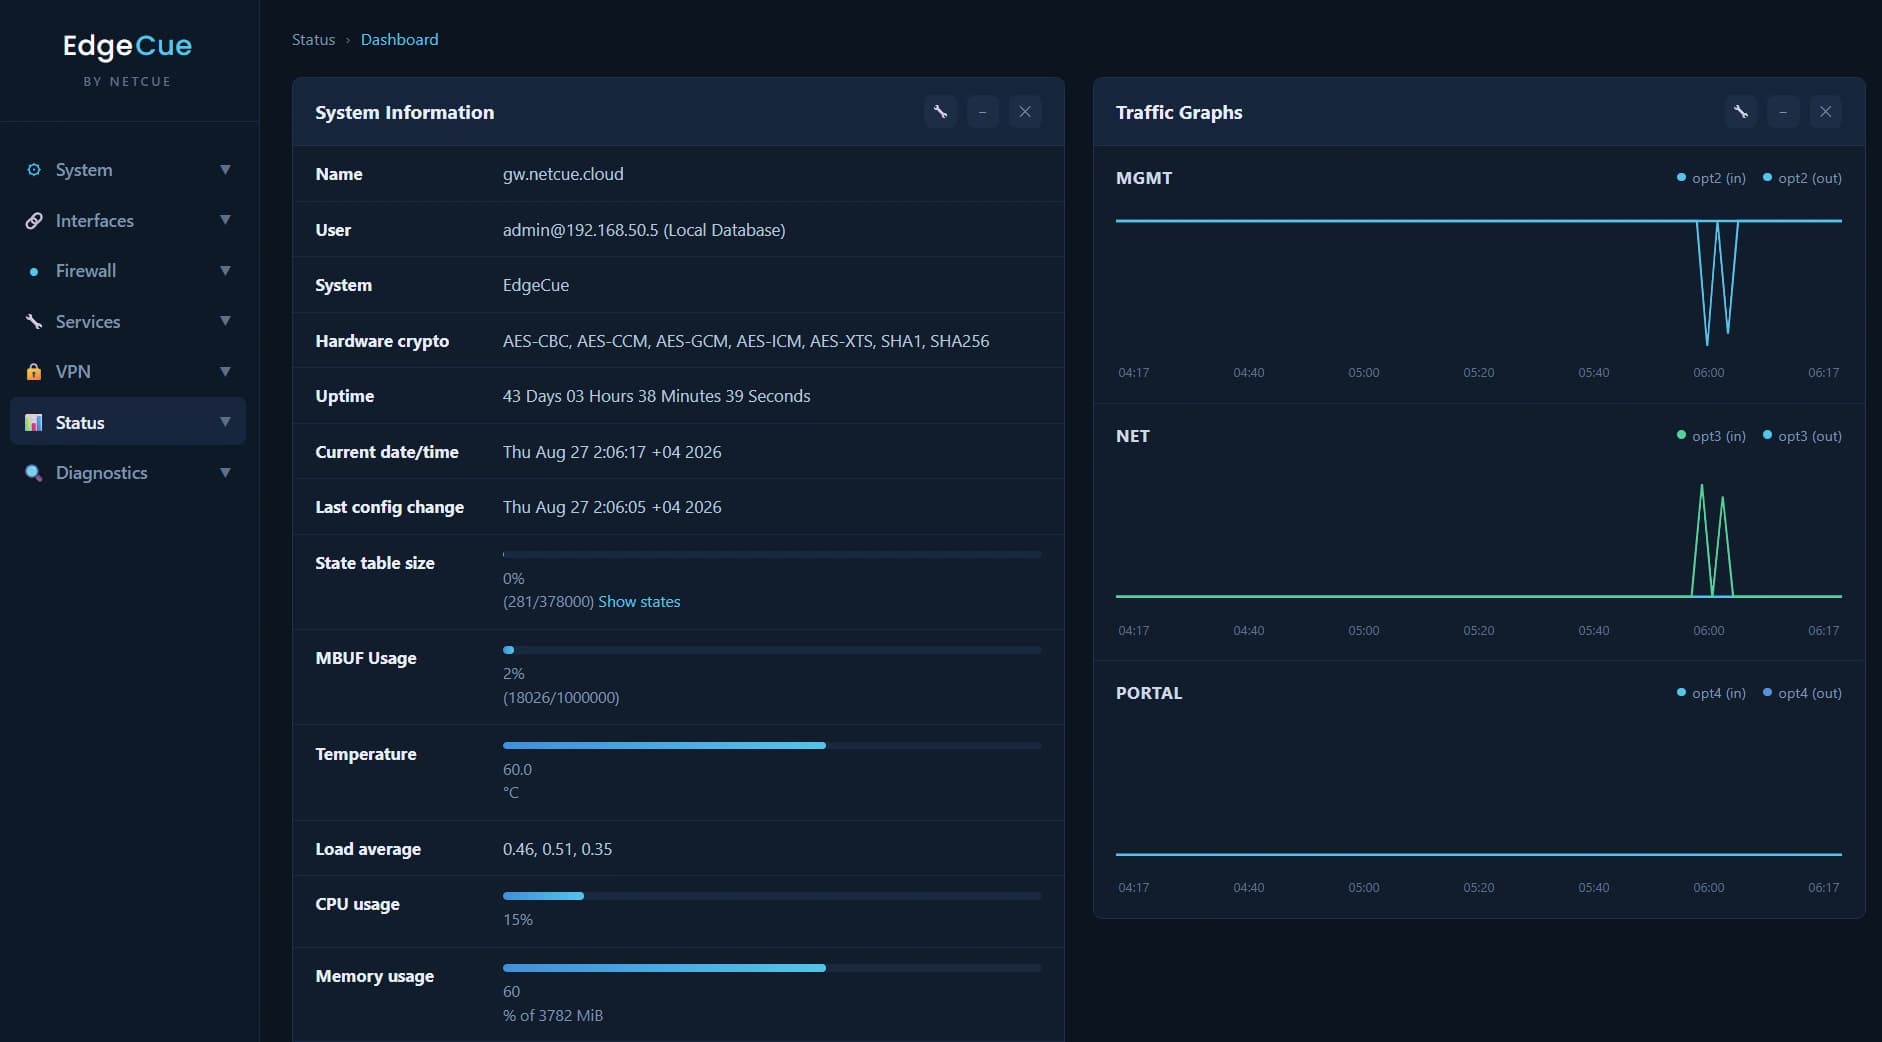
Six Pillars of HSIA Gateway
Captive portal, voucher and Guest WiFi are at the core. You also get DHCP, DNS and firewall, with Zenarmor as an add-on if you want it. Same software on every model from EC-500 to EC-10000.
01 — Captive Portal Authentication
You decide who gets on, how they log in and what they can do. One box can handle from 50 up to 10,000 devices.
Active Directory (AD) Integration
Staff and students authenticate with existing corporate or institution credentials — no separate passwords, no friction. Automatic VLAN assignment per AD group enables network segmentation by department, role, or building. Fully compatible with Microsoft AD, Azure AD, and OpenLDAP.
Voucher & Time-Limited Access
Generate, print, and manage time-limited voucher codes for temporary network access — hotels, conference centers, co-working spaces, and staff accommodation guest management. Set per-voucher bandwidth limits, session duration, and concurrent device caps. Bulk generation with CSV export for front-desk operations.
RADIUS Authentication & Accounting (802.1X)
Full RADIUS support via NETCUE RADIUS engine or external RADIUS servers including AccessCue. Centralize user authentication across multiple EdgeCue appliances. Complete session accounting — start, stop, and interim records — for billing, compliance, and usage auditing. Supports MSCHAPv2, EAP-TLS, PAP, and CHAP.
02 — Multi-WAN Failover & Load Balancing
In the UAE one internet line is rarely enough. EdgeCue can use several lines at once and keep you online even if one provider goes down.
Automatic Failover (Seconds, Not Minutes)
Gateway monitoring via ICMP, TCP, and HTTP probes detects WAN outages within seconds and reroutes all traffic to the next available link — invisibly, without dropping user sessions. Configurable failback rules return to preferred links when they recover.
Intelligent Load Balancing
Distribute outbound sessions across WAN links using weighted round-robin, least-connections, or sticky-session algorithms. Maximize the aggregate bandwidth of all your ISP connections simultaneously — run three 500Mbps links as effective 1.5Gbps throughput.
Policy-Based Routing
Route specific traffic types — VoIP, video conferencing, critical SaaS apps — always through a preferred WAN. Send general browsing across other links. Full granular control without complex CLI configuration.
Real-Time WAN Analytics
Live dashboard showing per-WAN status, latency, packet loss, and throughput. Historical graphs for ISP SLA tracking. Exportable reports for ISP fault claims and capacity planning.
03 — VPN Connectivity
Connect offices, remote workers and cloud securely. We support the main VPN protocols so you do not need to change what you already have.
IPSec Site-to-Site
Industry-standard IPSec tunnels between branches, data centers, or cloud VPCs. IKEv1 & IKEv2, compatible with Cisco, Fortinet, MikroTik, Palo Alto. Pre-shared key and certificate-based auth.
WireGuard®
Modern, high-performance VPN with minimal overhead and exceptional throughput. Faster key exchange and reconnection than legacy protocols — ideal for site-to-site and remote workers.
OpenVPN Remote Access
SSL/TLS remote access for roaming users. Clients for Windows, macOS, iOS, Android. Certificate or username/password auth with optional MFA integration.
04 — Firewall & DNS Threat Filtration
Block phishing and malware before they reach users. We check at DNS level and at the network edge.
Stateful Packet Inspection Firewall
Granular rule management — control traffic by source, destination, port, protocol, interface, VLAN, time schedule, and geographic region. Firewall aliases and groups simplify management of large enterprise rule sets across complex multi-VLAN environments.
DNS-Based Threat Filtration
Real-time threat intelligence feeds block DNS resolution for known malware C2 servers, phishing domains, spam sources, and botnet infrastructure. Threat feed subscriptions are updated multiple times daily with zero manual intervention.
Content & Category Filtering
Block web categories — adult content, gambling, social media, streaming, P2P — per VLAN, user group, or time of day. Compliant with UAE TRA internet usage regulations and corporate acceptable use policies.
GeoIP Blocking & Country Restrictions
Block all traffic from specific countries in a single rule. Protect against geographically concentrated attack campaigns, prevent unauthorized access from high-risk regions, and address data sovereignty requirements.
05 — Zenarmor NGFW Plugin (Optional, Subscription)
Add application control and inspection only where you need it. Zenarmor is a paid add-on. It lets you check encrypted traffic and filter apps per site without swapping hardware.
Deep Packet Inspection (DPI)
Identify and control 1,400+ applications regardless of port or encryption — social media, streaming, cloud storage, collaboration tools, gaming, and custom application signatures. Block or throttle specific apps without affecting other traffic on the same port.
AI-Powered Threat Intelligence
Machine learning–based threat detection identifies anomalous behavior, zero-day threats, and advanced persistent threats (APTs) that signature-based detection misses. Cloud-backed intelligence with real-time updates across the NETCUE global threat network.
Application Analytics & Reporting
Visual dashboards showing which applications consume the most bandwidth, which users represent security risk, and trending patterns over time. Exportable reports for compliance, executive briefings, and capacity planning.
TLS / SSL Inspection
Inspect encrypted HTTPS traffic to catch malware, data exfiltration, and policy violations hidden inside SSL tunnels — without breaking the legitimate user experience. Certificate management is automatic.
06 — Advanced DHCP, DNS Resolver & IPS/IDS
Manage IP addresses, run encrypted DNS and block intrusions with Suricata. All from one box.
Advanced DHCP Server
DHCP scopes per VLAN, static MAC-to-IP mappings, lease monitoring, DHCP relay agent, DHCPv6, and custom option sets. Full lease table visibility and exportable for inventory audits.
Unbound DNS Resolver
DNS-over-TLS (DoT), DNS-over-HTTPS (DoH), DNSSEC validation, split-horizon DNS, local overrides, and recursive resolution. Privacy-preserving and performant for large user populations.
Suricata IPS / IDS Engine
40,000+ detection rules from Emerging Threats and Snort community feeds. Blocks confirmed threats inline (IPS mode), alerts on suspicious patterns (IDS mode). Custom rules for environment-specific threat profiles.
Network Monitoring & Alerting
Live traffic graphs, top-talker identification, bandwidth per interface/client/application. SNMP v2/v3 export for Zabbix, Grafana, or PRTG. Email, Slack, and webhook alerting for critical events and threshold breaches.
Choose Your EdgeCue Model
Five purpose-built appliances sharing the same EdgeCue software platform. Scale up without retraining.
| Specification | EC-500 | EC-1000 | EC-3000 Popular | EC-5000 | EC-10000 |
|---|---|---|---|---|---|
| Firewall Throughput | 500 Mbps | 1 Gbps | 3 Gbps | 5 Gbps | 5 Gbps |
| WAN Ports | 2× GbE | 2× GbE | 2× GbE | 2× GbE | 2× GbE |
| LAN Ports | 2× GbE | 2× GbE | 4× GbE + 2× SFP+ | 4× GbE + 4× SFP+ | 4× GbE + 4× SFP+ |
| Devices | ≤ 200 | < 1,000 | < 3,000 | < 5,000 | ≤ 10,000 |
| VPN Throughput | 350 Mbps | 700 Mbps | 2.1 Gbps | 3.5 Gbps | 3.5 Gbps |
| Captive Portal | ✓ | ✓ | ✓ | ✓ | ✓ |
| RADIUS Auth | ✓ | ✓ | ✓ | ✓ | ✓ |
| IPS / IDS | ✓ | ✓ | ✓ | ✓ | ✓ |
| Zenarmor NGFW (Optional) | Optional | Optional | Optional | Optional | Optional |
| HA / Redundancy | — | — | Active-Passive | Active-Passive | Active-Active |
| NexusCue Management | ✓ | ✓ | ✓ | ✓ | ✓ |
| Form Factor | Desktop | 1U Rack | 1U Rack | 1U Rack | 1U Rack |
| Pricing | Get Quote | Get Quote | Get Quote | Get Quote | Get Quote |
All models ship pre-configured with EdgeCue firmware. Custom hardware specifications available on request for the GCC market. Contact our Dubai team for volume pricing.
EdgeCue Across Every Sector
Staff Accommodation
Manage Wi-Fi for thousands of residents with captive portal vouchers, per-user bandwidth fairness, and hotspot sharing prevention. Deployed across Dubai, Sharjah, Abu Dhabi, and Oman.
Universities & Schools
AD-authenticated student and faculty networks with content filtering, per-department VLAN segmentation, and safe internet policies. Compliant with UAE Ministry of Education guidelines.
Hospitality & Hotels
Branded guest splash pages, room-linked vouchers, PMS integration-ready, per-tier bandwidth shaping, and multi-WAN reliability for uninterrupted guest Wi-Fi.
Corporate & Enterprise
Secure site-to-site VPN between branches, zero-trust VLAN segmentation, AD SSO for staff, and NGFW protection for corporate assets across multi-site UAE operations.
Healthcare
Separate clinical, administrative, and guest VLANs, compliance-ready logging, secure remote IT access, and IPS protection for medical device network isolation.
ISPs & Service Providers
Managed CPE deployment for ISP customers, multi-tenant RADIUS billing integration, bandwidth policy enforcement, and centralized NexusCue monitoring at scale.
EdgeCue is Stronger Together
NexusCue
Manage all EdgeCue appliances remotely — push firmware, monitor health, access consoles, and respond to alerts without site visits.
Learn NexusCueAccessCue
Use AccessCue as the RADIUS backend — centralize user auth, session accounting, and subscriber data across all EdgeCue sites in one SaaS dashboard.
Learn AccessCueFlowCue
Deploy FlowCue upstream for 10 Gbps WAN aggregation on 15,000-user sites. EdgeCue handles security and captive portal; FlowCue owns the WAN layer.
Learn FlowCueReady to Deploy EdgeCue?
Our Dubai-based team will design the right EdgeCue model for your site — whether it's a 50-user branch or a 10,000-device campus network.